Start With What Was Downloaded and Run
Steam malware reports concern particular programs, builds and installers. BlockBlasters, PirateFi, Chemia and Sniper: Phantom's Resolution illustrate different delivery routes documented in 2025. A familiar storefront or an existing game library entry cannot, by itself, establish what a later executable does.
If you recognize a named game, record when you installed it, whether you launched it and any external installer you ran. Stop opening the suspicious program while checking the incident. Downloading a file, executing it and confirming account theft are different facts; describe what actually happened rather than running it again to find out.
Illustrative cover: Valve's June 2023 Steam client screenshot. The games pictured are unrelated to the malware cases discussed here.
Four Cases With Different Delivery Routes
The original reports support specific findings. They do not establish that every affected player ran the same payload, that every later game update is malicious or that all four incidents used an identical attack path.
| Game and dated source | What the report documents | Important distinction |
|---|---|---|
| BlockBlasters G DATA, September 22, 2025 | Malicious files in the August 30 patch, Build 19799326; a backdoor and StealC | A game update was the delivery route. An earlier version or positive review did not establish the later build's behaviour. |
| PirateFi SECUINFRA Falcon Team, March 6, 2025 | Vidar identified through the researchers' dynamic analysis and YARA matches | The researchers assessed it as a deliberate malware-distribution attempt, rather than a legitimate game that was later compromised. |
| Sniper: Phantom's Resolution Bill Toulas, March 21, 2025 | Players were directed to an external GitHub demo installer; the report attributes installer analysis to users | The external download route matters. A Steam listing did not make the separately hosted installer trustworthy. |
| Chemia PRODAFT public report added July 23, 2025 | A compromised game executable distributing Fickle Stealer and HijackLoader; Vidar also appears in the published indicators | Malware ran alongside the legitimate application. Listing several families does not establish that every installation ran all of them simultaneously. |
In G DATA's BlockBlasters analysis, the patch collected Steam login metadata, browser-related information and wallet data. The report also describes adding a payload directory to Defender's exclusions and then launching the game. That helps explain why a playable-looking result is not sufficient reassurance after suspicious behaviour.
SECUINFRA's PirateFi research identified repeated file changes and concluded that the package was intended to infect players. Its proposed improvements to Valve's review process are the researchers' opinion, separate from their identification of Vidar.
For Sniper: Phantom's Resolution, the contemporary BleepingComputer report describes an external installer named Windows Defender SmartScreen.exe. That filename did not make it a Microsoft security component. The article reports that GitHub removed the repository and Valve removed the game; it attributes the technical observations to users who examined the installer.
PRODAFT's Chemia report attributes the compromise to LARVA-208 and describes malicious binaries embedded in the executable distributed through the platform. Its public file identifies two main payloads and supplies additional indicators. This is a different finding from assuming the game was always a fake application.
What Valve Reviews Before Release and Afterward
Valve reviews both the store presence and the product build before release. The Steamworks review documentation also says an approved game can be updated without going through that review again. The initial process therefore is not store-page-only, and approval is not a fresh review of every subsequent version.
The current Builds documentation adds a separate control: setting a build live on a released game's default branch requires additional authorization. It goes to the requesting Steamworks account's Steam Mobile Authenticator when configured, or otherwise to the associated phone by SMS.
That authorization concerns control of the publishing account. It is different from examining what the program does, and it should not be described as a guarantee that an authorized update is harmless. The public documentation does not establish the outcome of every internal security check in each historical case.
Updates are also how legitimate developers deliver fixes. These incidents support attention to the particular file and delivery route; they do not establish that permanently avoiding all updates is a reliable security strategy.
If You Installed or Ran a Suspicious Game on Windows
Keep the game name, installation and launch dates, security alerts and relevant messages. A store removal does not show whether local files remain, whether anything executed or whether credentials were already copied. Address the device and affected accounts separately.
- Stop launching the suspect game or installer. Avoid downloading replacement copies or following messages that ask you to disable protection to make it work.
- Update protection and run a full scan. Open Windows Security, choose Virus & threat protection, check Protection updates, then use Scan options → Full scan → Scan now.
- Consider Microsoft Defender Offline for suspected persistent malware. Under Scan options, select the offline scan. Save your work first: it restarts the PC and runs a quick scan in the Windows Recovery Environment.
- Read the results in Protection history. Review Allowed threats and antivirus exclusions, including entries you do not remember adding. Remove allowances or exclusions for the suspect program instead of allowing it again.
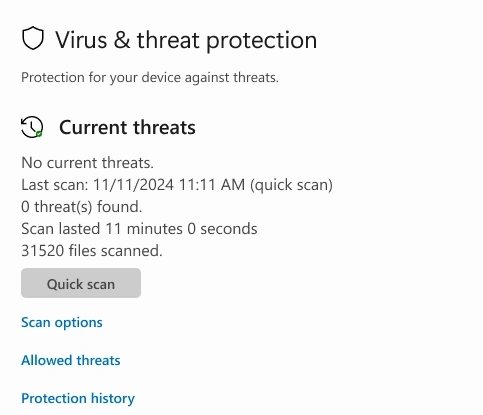
Open Microsoft's original Windows Security screenshot.
Microsoft's Windows Security guide explains these controls. A Full scan and Defender Offline are different scan modes; the offline option is not simply a full scan with the network turned off.
If detections recur or removal fails, follow Microsoft's malware troubleshooting guidance. It covers recurring components and recovery options for irreversible changes. Neither uninstalling a game nor one clear scan result can reverse data that an information stealer has already copied.
Secure the Email Account and Recover Steam Access
Device cleanup and account recovery solve different problems. A stolen password or session can remain relevant after the malicious program has been removed, so review the accounts you actually used on the affected computer.
Steam's stolen-account guidance instructs users to scan the computer, secure the associated email account and then recover Steam access once the computer and email are secure. If the email account is compromised, a Steam password change alone may leave the recovery channel exposed.
Use the relevant provider's official recovery route for each affected account. Enter credentials only on the provider's verified site, and never give a Steam password to someone claiming to be support. A direct message offering help is not proof of affiliation with Valve.
Use the FBI's Current Steam Malware Reporting Route
As checked on October 28, 2026, the FBI Seattle Division's victim-information form describes suspected targeting from May 2024 through June 2026. It names BlockBlasters, Chemia, Dashverse/DashFPS, Lampy, Lunara, PirateFi, Tokenova and Beyond the Dark.
That is the form's investigation scope, not a finding that every download caused a loss. Sniper: Phantom's Resolution is a separate reported case and is not named on the reviewed form. The reporting window also does not establish when the investigation began.
Prepare the game and dates, whether you played it, relevant contact usernames or messages, affected accounts and any transaction details that apply. Submit sensitive information through the official form rather than a public comment or an unsolicited direct message. The form also directs fraud reports to IC3.
The FBI warns against paying people who claim they can recover lost funds, including demands for additional fees or taxes. Reporting is voluntary and may help investigators; it is not a promise of recovery.
Before Trying an Unfamiliar Game or Demo
Keep protection enabled and treat requests to bypass a security alert as a reason to pause. Reviews, a familiar logo and a program that opens successfully are not substitutes for checking a suspicious installer or update. The external-download route in the Sniper report is especially relevant when a demo sends you away from its storefront.
Follow the publisher's verified distribution links, read security notifications from Steam and your protection provider, and keep any incident evidence before seeking help. If another person asks for a password, verification code or payment to fix the problem, verify the request through the provider's own support site.